Research agenda

Security for intelligence.
Intelligence for security.

Our research sits at the intersection of security, privacy, and artificial intelligence. We study how to make generative AI systems safer and more trustworthy—and how to use AI to strengthen security analysis.

01

Generative AI Security & Privacy

Protecting increasingly autonomous AI systems across the full security lifecycle.
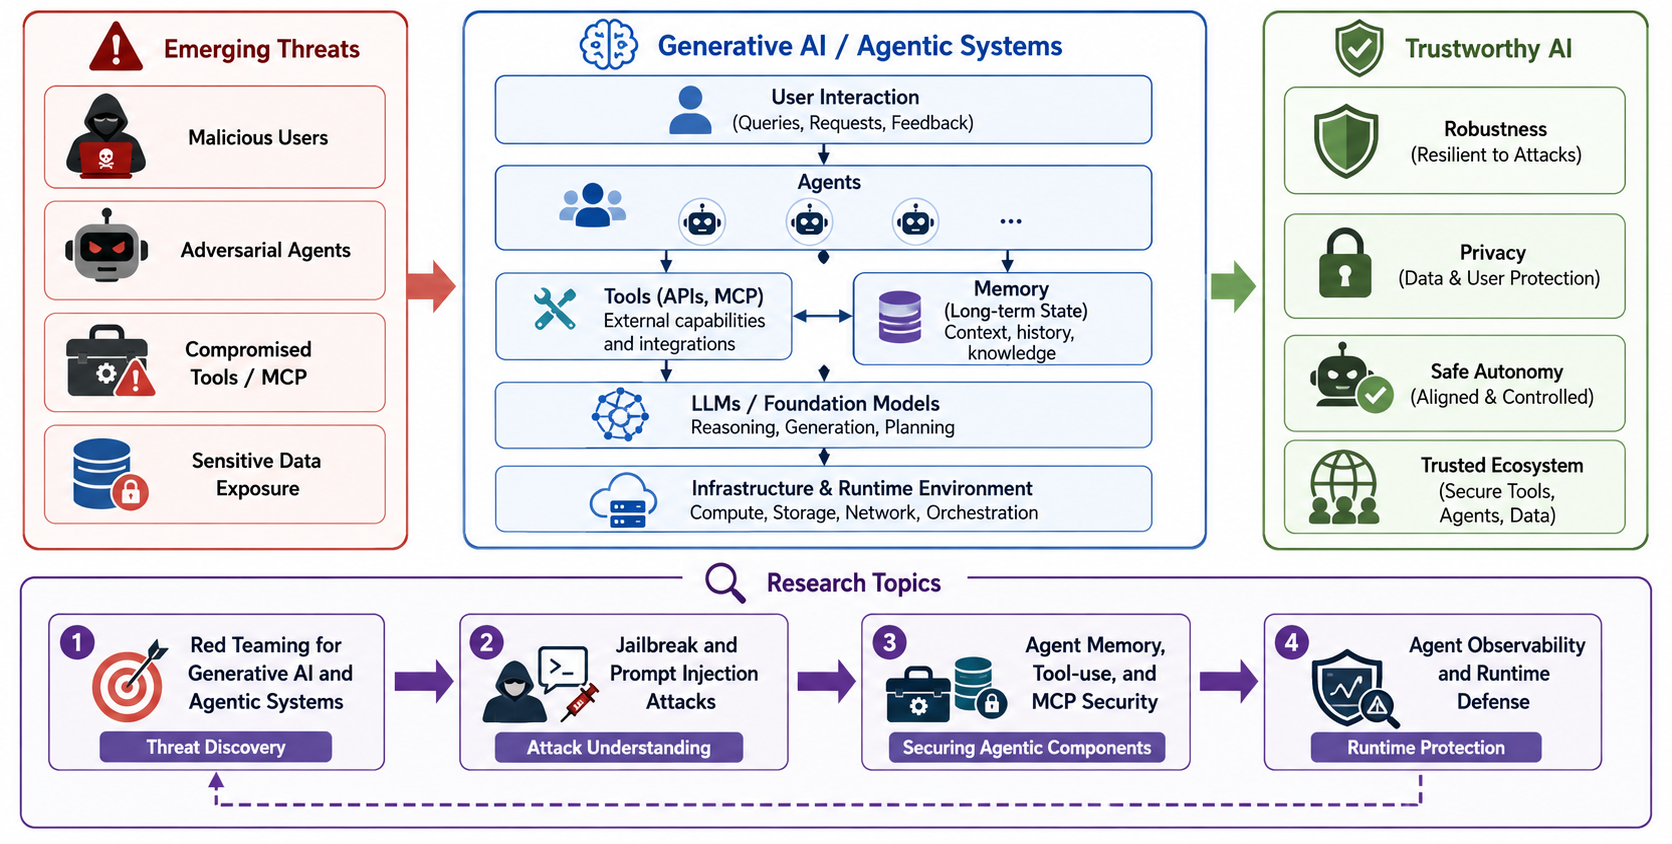
Research framework for generative AI security and privacy

Research scope

The growing autonomy and interactivity of generative AI systems are reshaping their security and privacy threat landscape, particularly as large language models are embedded in agentic systems with persistent state, external tools, and the ability to act in dynamic environments.

We identify and mitigate emerging risks—from uncovering hidden threats through black-box adversarial attacks, to systematically characterizing security properties, and ultimately enabling continuous protection at runtime.

Research topics04 focus areas
  • 01Red Teaming for Generative AI and Agentic Systems
  • 02Jailbreak and Prompt Injection Attacks
  • 03Agent Memory, Tool-use, and MCP Security
  • 04Agent Observability and Runtime Defense
02

AI Safety

Building confidence in synthetic media and the models that produce it.

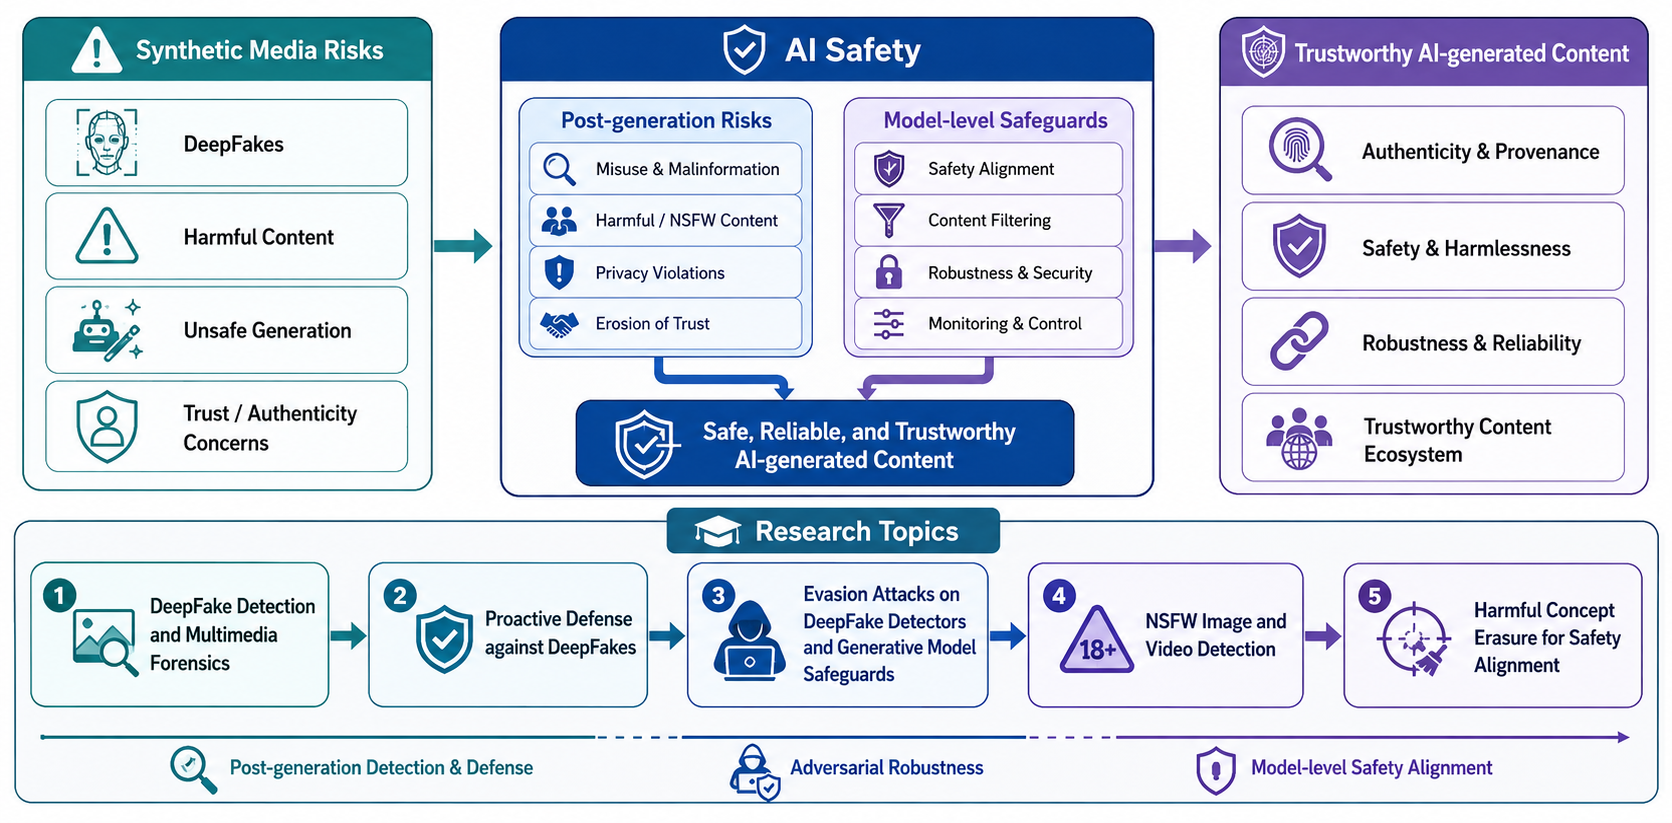
Research framework for AI-generated content safety

Research scope

The rapid advancement of generative AI has increased the realism, accessibility, and scale of synthetic media, creating growing concerns around content authenticity, harmful content, and the safety of generative models.

We study both post-generation risks and model-level safeguards: detecting and proactively defending against DeepFakes, understanding attempts to evade detection and safety mechanisms, and helping generative models recognize and suppress harmful concepts.

Research topics05 focus areas
  • 01DeepFake Detection and Multimedia Forensics
  • 02Proactive Defense against DeepFakes
  • 03Evasion Attacks on Detectors and Model Safeguards
  • 04NSFW Image and Video Detection
  • 05Harmful Concept Erasure for Safety Alignment
03

Generative AI for Security

Advancing intelligent vulnerability research for high-value systems.

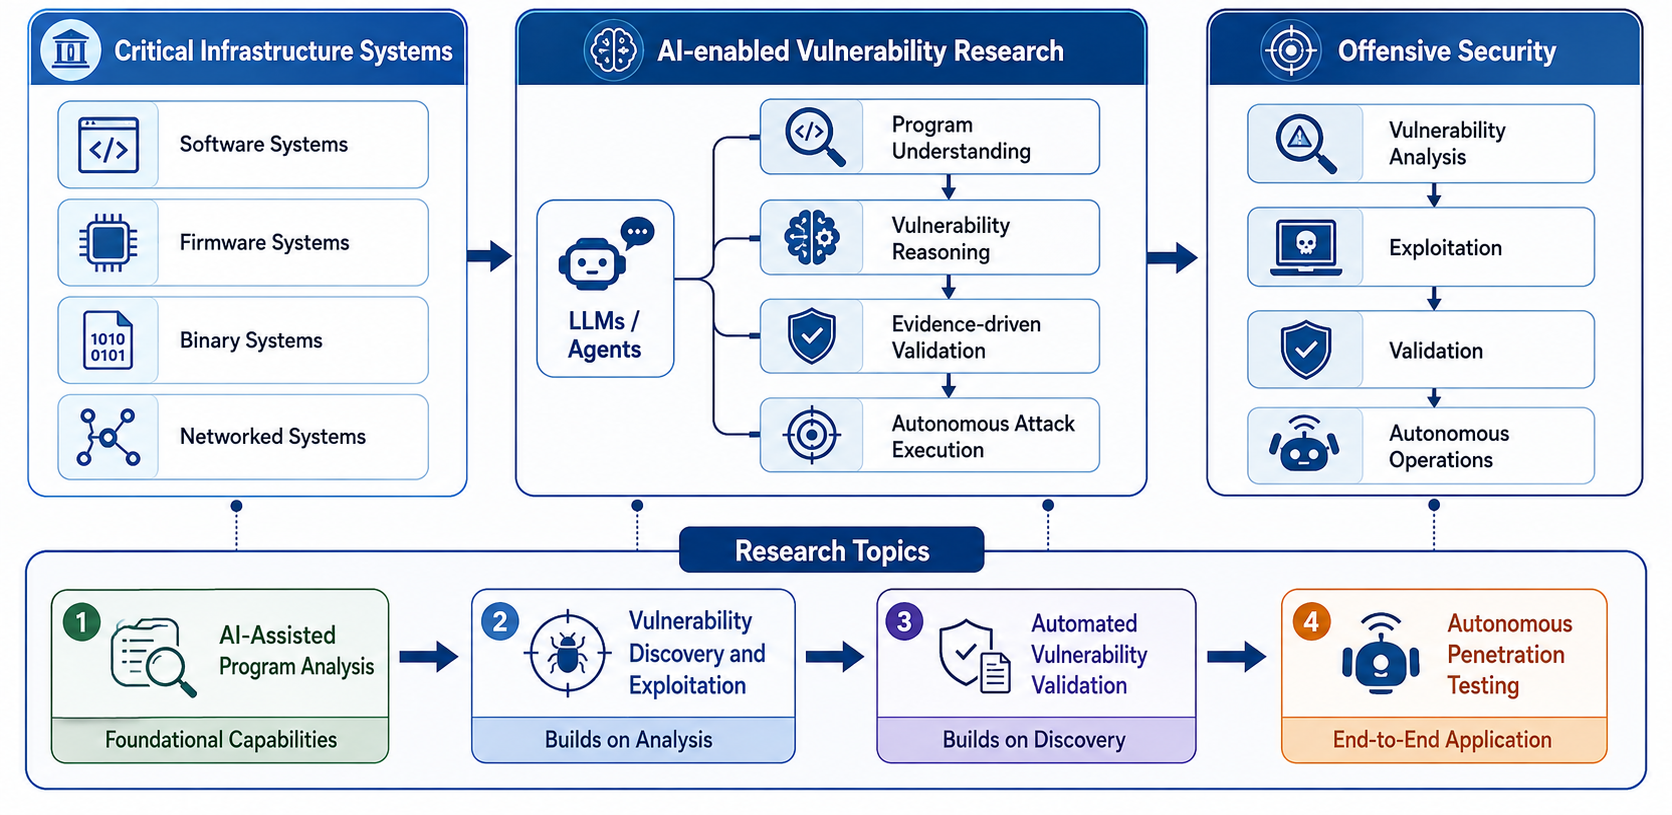
Research framework for generative AI-assisted vulnerability analysis

Research scope

The reasoning, coding, and tool-use capabilities of large language models and autonomous agents are opening new opportunities for vulnerability research in complex software, firmware, and networked systems that underpin critical infrastructure.

We combine program understanding, vulnerability reasoning, evidence-driven validation, and autonomous attack execution to improve the efficiency, depth, and autonomy of security analysis.

Research topics04 focus areas
  • 01AI-Assisted Program Analysis
  • 02Vulnerability Discovery and Exploitation
  • 03Automated Vulnerability Validation
  • 04Autonomous Penetration Testing

Research support

Selected funded projects.

Research programs supporting our work in AI security, DeepFake forensics, and trustworthy intelligent systems.

PI

国家自然科学基金面上项目

面向文生图大模型生成内容的无害化安全技术研究

01
PI

企业横向合作项目

基于生成式人工智能的Agent构建关键技术研究

02
PI

XXX重大专项项目

XXX突控关键技术研究

03
Co-PI

国家重点研发计划项目

超大规模网络中恶意流量跨域监管与智能处置技术及应用验证

04
View completed projects Hide completed projects 02 archived
PI

国家自然科学基金青年项目

面向开放环境下的重点人物伪造视频取证关键技术研究

05
Co-PI

国家重点研发计划青年科学家项目

人工智能安全防御与评估技术

06